Account takeover (ATO) attacks, where unauthorized users gain access to someone's digital accounts, have become increasingly sophisticated and frequent, and rates of attack have increased in 2023. We explore some of the vectors that will be come more prolific in 2024, and some mitigating controls.
Here are the latest stats from 2023:
- There was a 354% increase in ATO attacks compared to the previous year, according to Sift’s Q3 2023 Digital Trust & Safety Index.
- A report by Security.org and Deduce revealed that 22% of adults in the U.S. have experienced account takeover attacks, affecting around 24 million households.
- According to the same Sift report from Q3 2023, 73% of consumers hold the brand responsible for ATO attacks and the security of account credentials.
- Sift’s Q3 2023 Digital Trust & Safety Index also found that only 43% of individuals affected by account takeovers were informed by the concerned company about their compromised information.
- SpyCloud's 2023 Annual Identity Exposure Report highlights that there was a 72% rate of password reuse among users involved in two or more breaches in the last year, marking an 8% increase from 64% the previous year.
- The Aite-Novarica 2022 U.S. Identity Theft report states that 24% of ATO fraud victims had their contact details altered post-incident, a tactic used by fraudsters to reroute communications to themselves instead of the legitimate account holder
The Top 3 attack vectors for ATO in 2024
Session Hijacking/MFA By-pass
Session hijacking has to be the most prolific attack in the last year, with many high profile platforms falling to session hijacking.
The attack is very simple, a legitimate user authenticates with an application, receiving a session token/cookie, the user may have performed 2FA/MFA in that process, thus giving the perception that the session/cookie can be highly trusted.
This highly privileged and often long life session is now a prized piece of data for a cyber criminal to exfiltrate and steal, giving open access to the applications sensitive data or actions to be able to perform e.g executing a bank withdrawal or exfiltrating Personally Identifiable Information (PII) data like date of birth, addresses, and list of transactions.
How does a session get stolen or hijacked?
- 3rd party browser extensions, can sniff out sessions on domains
- Rooted or malware infected mobile devices and OS can intercept network requests within devices
- Public WiFi or unsecured networks - unsecured networks allow for Man in the middle attacks which can impersonate popular social login providers (like Google or Facebook) as an example
- Poorly implemented customer support systems - In a recent high profile session hijacking attack, a browser session recorder contained these prized sessions, and these sessions were breached and used for further lateral movement
How to mitigate session hijacking risk?
- Up-lift step-up authentication to use phishing resistant factors like FIDO2 Passkeys, which not only offer security improvements but great usability and user experience for your customers
- Constantly evaluate the risk of sessions or user actions, and issue step-up authentication flows on high risk transactions
- Reduce the time to live/time out of sessions
- Detect malware on devices and decline transactions that have been initiated from infected devices
Credential Stuffing/Re-used passwords
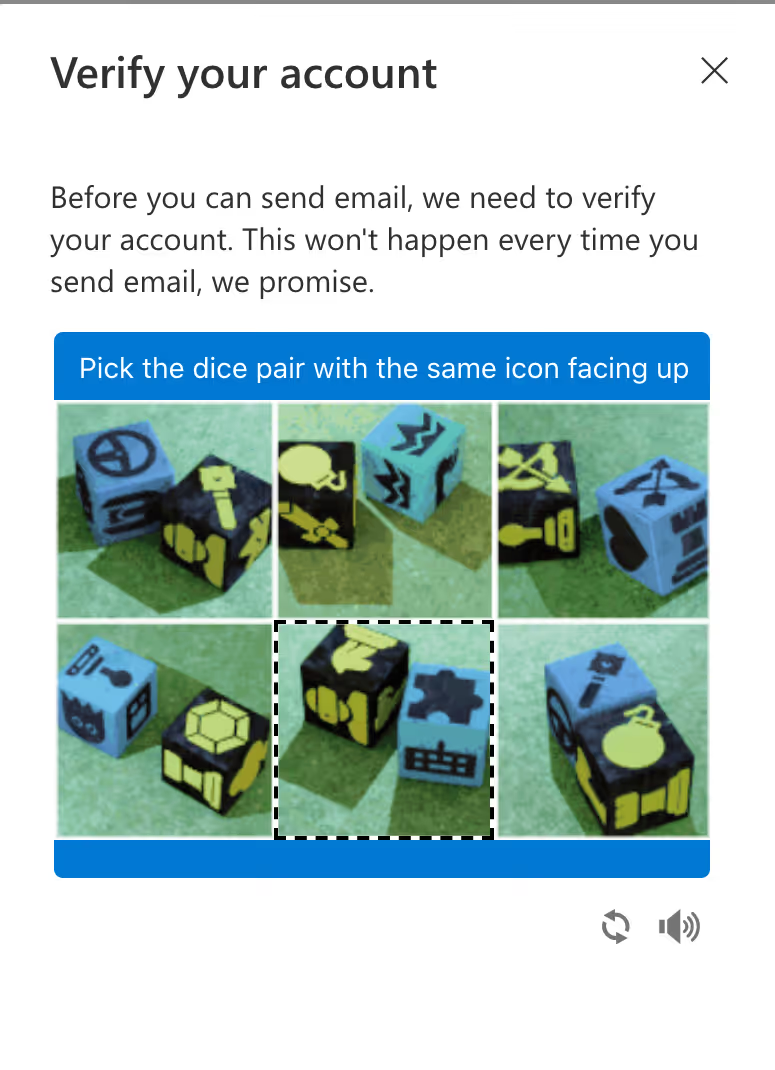
This is is a tried and true ATO attack vector that is relatively cheap to execute and still yields a great success rate, these attacks have evolved rapidly to evade controls such as bot protection CAPTCHAs, through next generation credential stuffing bots.
These next generation of credential stuffing bots exploit the poor UX of frustrating captcha riddles, in some instances creating attacks that put every customer even good ones through end-less captcha loops, forcing platforms to reduce thresholds to reduce good customer impact. Other techniques involve being able to easily solve CAPTCHAs through generative AI and performing low and slow attacks that sit under thresholds that trigger challenges.
On-top of poor mitigation techniques, the fundamental flaws in passwords as an authentication factor exists via the following:
- Re-use of passwords - offering passwords as primary option even with password complexity requirements is null and void because the majority of end-users just re-use passwords, and it only takes 1 data breach or a successful phishing attempt to create a domino effect for a cyber criminal to exploit
- Reluctance to implement MFA/2FA factors - The issue is 2 fold, a reluctance of platforms to implement MFA across the board and the reluctance to enforce these MFA controls within applications.
- Typical excuses that come which re-enforce the reluctance is the lack of regulatory/compliance requirements, impact to customers and the lack of resources to prioritize the roll out of strong authentication flows to customers
How to mitigate credential stuffing/re-used password risk?
- MFA/2FA is your primary line of defense, enforce MFA particularly on new and un-trusted devices
- Go passwordless - Remove the password box completely and couple it to the introduction of passkeys
One time password (OTP) Code Phishing
One-Time Password (OTP) code phishing is a sophisticated form of phishing where attackers aim to steal the temporary authentication codes that are often used as part of a two-factor authentication (2FA) system. Unlike traditional phishing, which typically targets usernames and passwords, OTP phishing focuses on intercepting or deceiving users into revealing their time-sensitive codes.
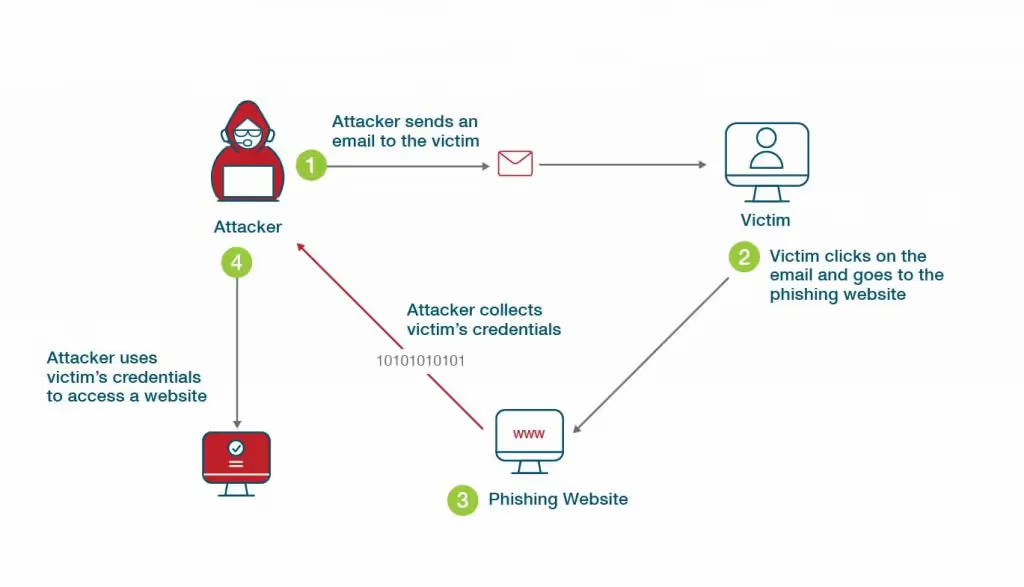
Here's how it typically works:
- Initial Compromise: The attacker tricks the victim into providing their username and password. This is often done through a standard phishing attack, such as a fake login page for a service the user trusts.
- OTP Request: When the victim attempts to log in with their credentials, the legitimate service sends an OTP to the victim, as part of its standard 2FA process.
- Phishing for the OTP: At this point, the attacker, having the victim's login credentials but lacking the OTP, will craft a follow-up phishing message. This message often urges the victim to share the OTP they just received, sometimes under the guise of "verifying their identity" or "preventing unauthorized access" to their account.
- Code Interception and Misuse: If the victim falls for this second phase of the attack and shares their OTP, the attacker can use it to complete the login process. Since OTPs are generally time-bound, the attacker acts quickly to gain access to the victim's account.
How to mitigate OTP code phishing risk?
- Phase out phish-able authentication factors like passwords, pins, and OTPs
- Uplift customers into Passkeys/FIDO2 security keys, and deprecate use of OTPs
- Educate customers on the risks of phishing and how to spot common phishing techniques
- Opt-for end to end encrypted message channels to deliver OTPs like WhatsApp for business